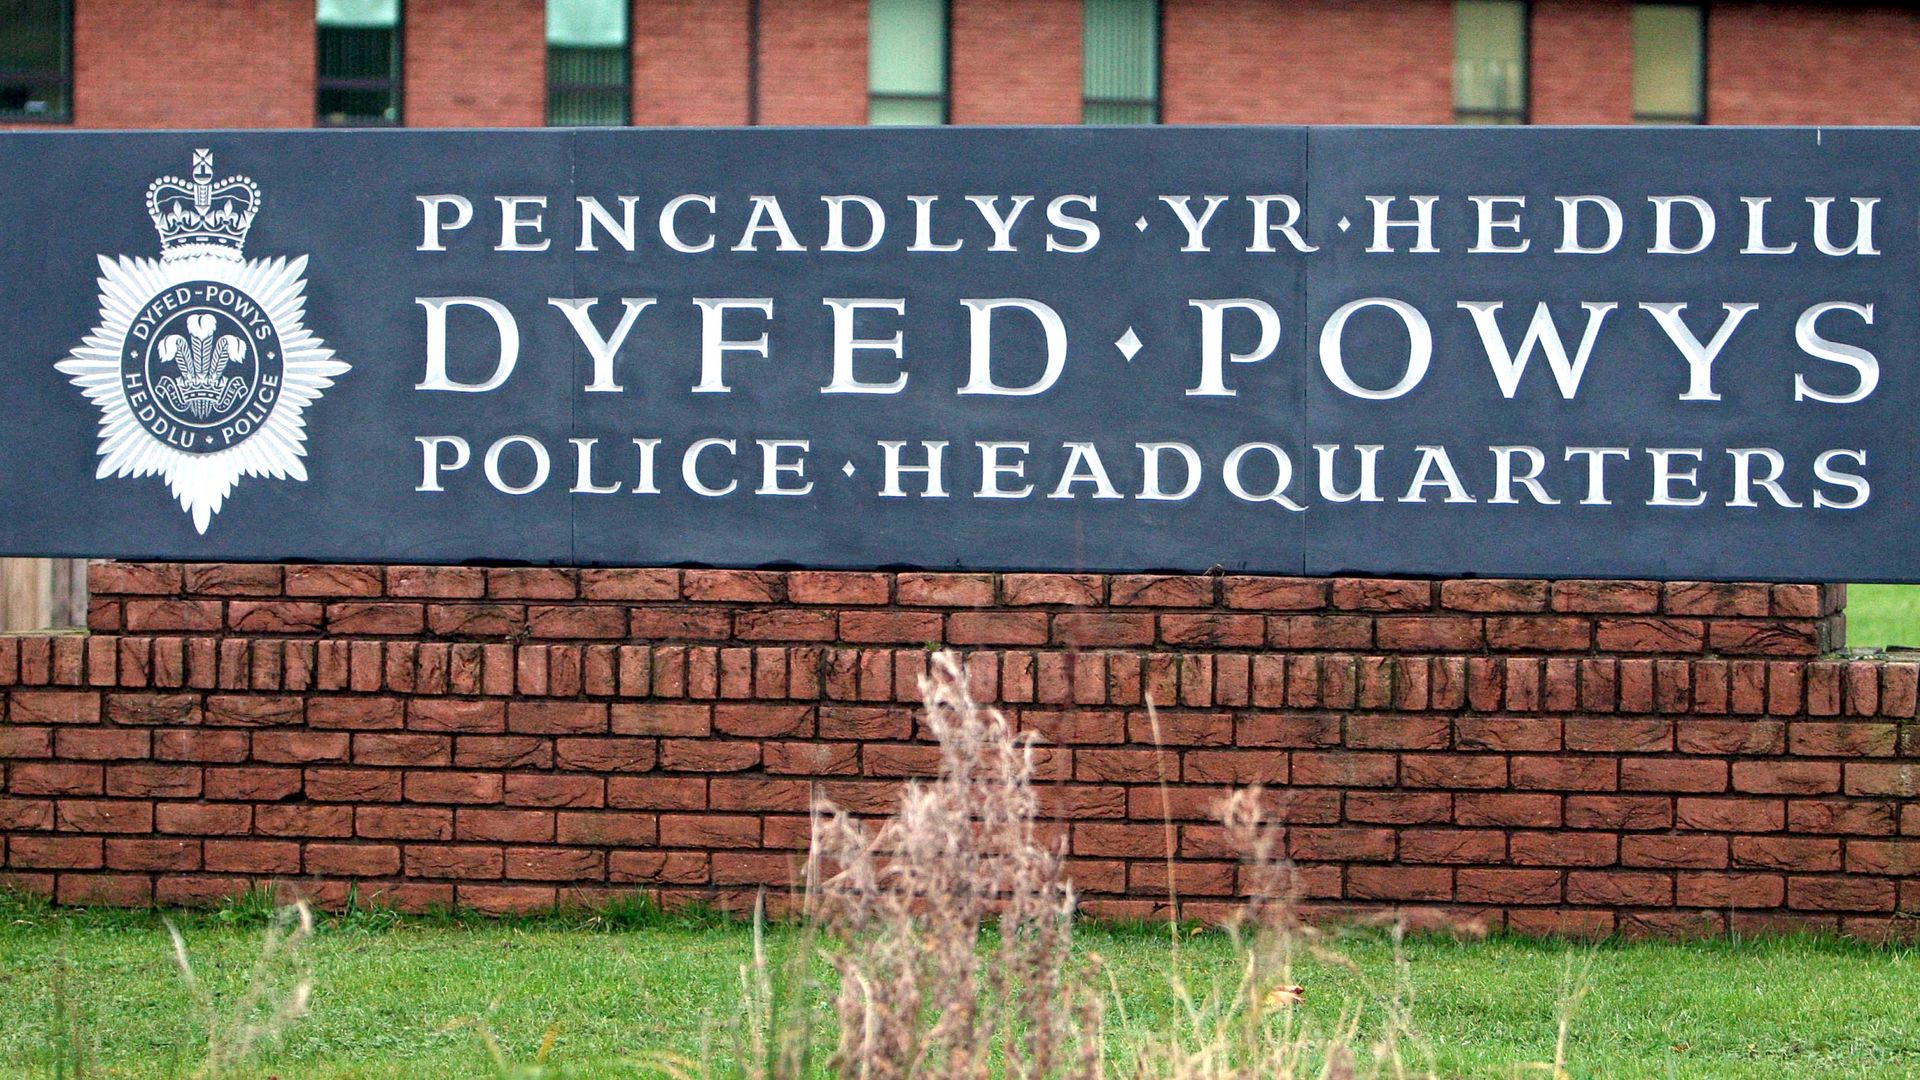
When the digital perimeter of Dyfed-Powys Police buckled under a targeted cyber attack, the initial institutional response followed a familiar, well-worn script. Non-emergency systems stuttered offline, officials scrambled to contain the narrative, and public reassurances emphasized that core emergency response functions remained insulated. Yet, beneath the standard police statements lies a far more unsettling reality. Law enforcement agencies across the United Kingdom are operating on digital foundations that are chronically underfunded, structurally fragmented, and increasingly vulnerable to malicious intrusion.
The incident at Dyfed-Powys—which compromised specific staff data tied to the Police National Legal Database (PNLD) including names, organizational affiliations, and work email addresses—exposed an uncomfortable truth about public sector cybersecurity. While public-facing panic was averted by assertions that confidential victim, witness, and offender records stayed untouched, the breach of internal personnel datasets highlights a systemic exposure. In modern espionage and cybercrime, personnel data is not merely administrative collateral. It is a primary vector for social engineering, credential harvesting, and lateral movement inside high-value government networks.
To understand why a territorial force policing over 500,000 residents across rural and urban Wales became a soft target, one must examine the architecture of British policing itself. Unlike centralized national security apparatuses, UK policing is historically regionalized into dozens of autonomous or semi-autonomous forces. Each maintains its own IT procurement cycles, digital security budgets, and infrastructure priorities. This decentralization creates an uneven security posture. While metropolitan giants can invest heavily in dedicated security operations centers and threat intelligence units, smaller regional forces frequently struggle to bridge the widening gap between legacy hardware and the sophisticated threat actors targeting public infrastructure.
Legacy architecture remains the Achilles' heel of municipal defense. Many police networks rely on custom, aging applications that cannot easily patch vulnerabilities without disrupting mandatory operational duties. When an update cycle takes months or requires expensive contractor interventions, threat actors move faster than bureaucratic procurement committees. The adversary only needs a single overlooked endpoint or an unpatched VPN appliance to establish a foothold.
Consider the operational friction introduced when non-emergency systems are forced offline. Police work relies heavily on data accessibility—checking intelligence logs, processing administrative filings, coordinating vehicle telemetry, and communicating across regional boundaries. When those systems go dark, officers are forced to revert to manual workarounds, radio traffic, and paper logs. This friction degrades operational tempo at best and introduces critical visibility gaps at worst.
Furthermore, the fallout from compromises involving the Police National Legal Database points to a broader structural hazard. The PNLD serves as a central repository for criminal justice guidance, legislation, and operational law. While database administrators were quick to clarify that sensitive investigative files were separate, the exposure of internal profiles creates immediate risks for personnel. In an era where targeted harassment, doxxing, and credential stuffing are industrialised cybercrime models, compromising the digital identities of criminal justice workers carries profound security implications.
Blaming individual regional forces for these vulnerabilities misses the mark. Expecting dozens of independent regional police commands to maintain elite, enterprise-grade cybersecurity postures independently is a systemic failure of policy. The financial overhead required to maintain continuous threat hunting, zero-trust architecture, and 24/7 security monitoring far exceeds the regional council tax and central grant allocations that sustain many local forces.
Fixing this structural rot requires more than temporary incident remediation or a polite request for better employee password hygiene. It demands a hard look at consolidation and centralized digital defense. If law enforcement is expected to operate as a unified defense against transnational cybercriminal syndicates and state-backed espionage groups, the digital infrastructure protecting them cannot remain decentralized and fragmented. Until public sector technology funding matches the aggressive sophistication of modern threat actors, incidents like the one in Wales will remain symptoms of a chronically exposed baseline.
The digital perimeter will be tested again. The next time, the outcome may not be contained to administrative records.