The cabin air always smells faintly of hot coffee and old wool just before pushback. If you sit near the wing, right where the aluminum curves into the housing of a Pratt & Whitney or a CFM engine, you can feel the low, steady thrum through your boots. It’s a mechanical heartbeat. Passengers lean their foreheads against double-pane glass, watching rain streak sideways across the runway, trusting that what happens next is a triumph of physics over gravity.
We forget that physics has a co-pilot now. Millions of lines of compiled logic sitting quietly in black boxes behind the cockpit bulkheads.
When news broke that a software bug had been discovered in the Boeing 737 Max 10—specifically within the engine anti-ice system—the regulatory response was swift and precise. The United States Federal Aviation Administration issued a formal stance: Not a safety concern.
To an engineer pouring over logic gates and failure trees, those words carry a very specific, mathematical meaning. They mean the probability is vanishingly small. They mean redundancy exists. They mean the system has a safe state.
To a passenger in row 24, watching the green lights reflect off the wet tarmac, those words sound like bureaucratic insulation.
Language matters. And when code meets cold air at thirty-five thousand feet, the distance between abstract regulation and human terror can be measured in milliseconds.
Consider a hypothetical scenario, one grounded entirely in the engineering realities of high-altitude flight. Imagine Elena, a systems integration lead who has spent eighteen years at a major aerospace component supplier outside Seattle. Elena doesn't write code to be clever; she writes code to survive a lightning strike, a sudden drop in barometric pressure, or a freak atmospheric pressure wave over the Dakotas.
Elena knows what happens when ice crystals begin to accrete on a sensor housing. It isn't cinematic. The warning lights don't flash in a dramatic neon cascade. Instead, a digital register flips from zero to one. A valve opens. Hot bleed air from the engine compressor is diverted to heat the cowl lip, keeping the throat of the intake clean so the turbine blades can breathe.
Now, imagine that the software governing that valve has a logical flaw. Under a very specific, narrow set of meteorological conditions—temperatures hovering just below freezing, high relative humidity, and specific engine power settings—the software might prematurely deactivate the engine anti-icing system before the hazard has cleared.
The regulator looks at this and says: Not a safety concern. Why? Because the pilots have manual override switches. Because secondary indicators will show rising engine vibration or pressure differentials. Because the crew is trained to recognize the symptoms of ice accumulation and manually cycle the system back on.
That is the engineering truth. It is logical. It is calculated.
It is also terrifyingly fragile when placed inside a cockpit already saturated with sensory inputs during a turbulent night approach into Chicago O'Hare.
We have built a world where complexity is the price of admission. A modern narrowbody aircraft is no longer just wings, fuel, and cables connected to pulleys. It is a distributed network of microcontrollers, sensors, and feedback loops, flying in formation at the speed of sound. Every software update is a promise that we can outsmart the weather, out-compute the wind, and manage the staggering weight of our own engineering ambition.
When a bug is found in that architecture, it forces an uncomfortable conversation about trust.
We entrust our lives to people we will never meet, writing code we will never read, overseen by regulators we will never see. We sit in molded plastic seats, eating stale pretzels, while billions of transistors make split-second decisions about our survival.
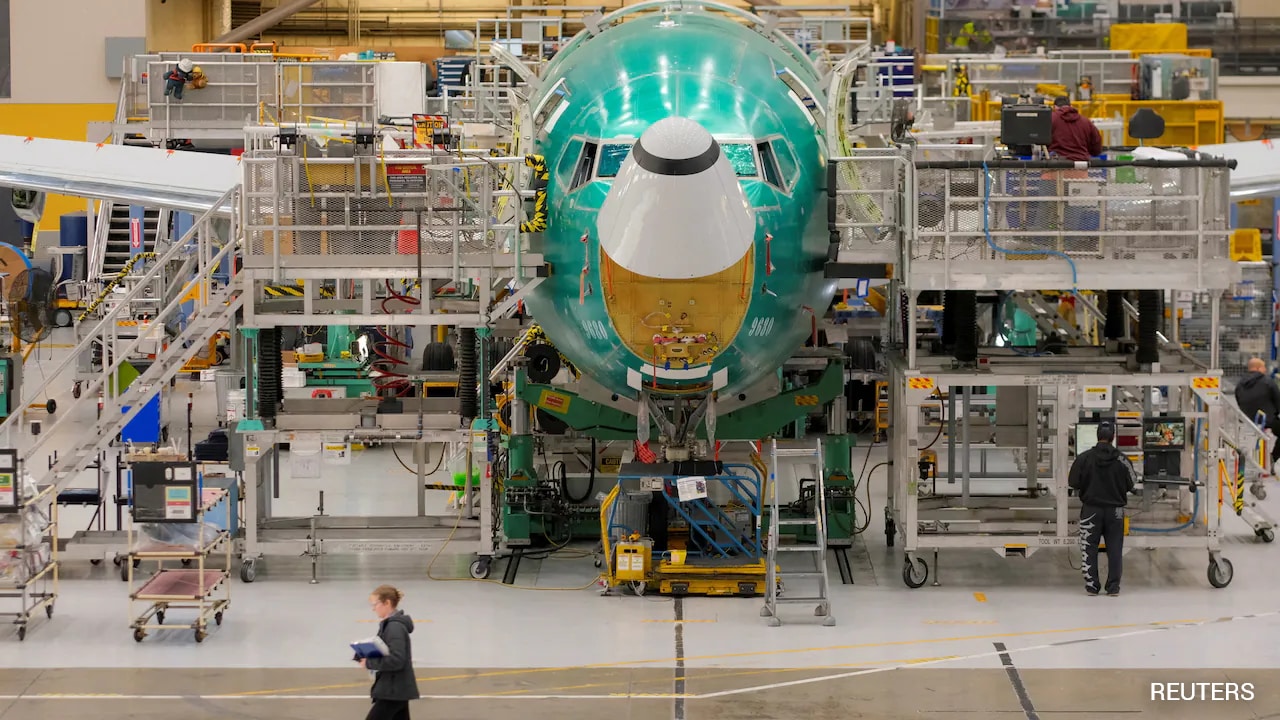
The Boeing 737 Max 10 is designed to be the backbone of domestic commercial aviation for the next three decades. It is stretched, efficient, and optimized down to the last drop of jet A fuel. It represents the pinnacle of modern industrial design—an economic necessity for airlines trying to squeeze profit margins out of crowded skies.
And yet, software is inherently human. It is written by tired developers drinking lukewarm Earl Grey at 2:00 AM. It is reviewed by committee. It is tested in simulators that can never quite replicate the chaotic, violent unpredictability of a real thunderstorm over the Rockies.
When the FAA declares a software anomaly safe, they are operating on a framework of risk management. They are balancing the statistical likelihood of failure against the immense operational disruption of grounding a fleet. They are right, in the spreadsheet sense of the word.
Yet, trust cannot be maintained by spreadsheets alone.
The real challenge facing modern aviation isn't fixing bugs before they trigger emergencies; it is bridging the empathy gap between the people who write the logic and the people who ride inside the aluminum tube. When a pilot flicks a switch to manually override an automated anti-ice cycle because a line of code failed, they aren't just executing a checklist. They are stepping into the breach left by human error, digital oversight, and regulatory calculus.
Next time you board an aircraft, look out the window at the sleek, curved composite structure of the wing. Listen to the whine of the auxiliary power unit winding down. Remember the invisible web of algorithms keeping you aloft.
The system holds. It almost always holds.
But as we push our machines higher, faster, and deeper into the realm of automated perfection, the margin for error shrinks to the thickness of a single line of code. And somewhere in the dark, thirty thousand feet above the earth, Elena's logic gates are clicking quietly away, waiting for the weather to turn.